White Tuque, Offensive Security Specialist
Toronto · Oct 2024 to Present
Black-box and grey-box penetration tests, red team and purple team assessments for 20+ enterprise clients plus standalone engagements, across web, API, mobile, networks and cloud. Operate Cobalt Strike and Havoc C2 on red team engagements. Built the red team and penetration-testing pipeline for a major Canadian insurer, with recurring adversary simulations and tabletop exercises. Review AI and agentic workflows for prompt injection, insecure tool use and excessive permissions. Lead engagements end to end and mentor interns on the offensive team.
ASEC, Penetration Tester
Toronto · May 2024 to Oct 2024
Application, API and network assessments for fintech and financial-services clients across Canada, the US, Australia and Europe, specializing in API and GraphQL security under Nick Aleks, author of Black Hat GraphQL and former Head of Security at Robinhood. Wrote a custom Nuclei template for each finding so clients could regression-test the fix in their own CI/CD pipelines.
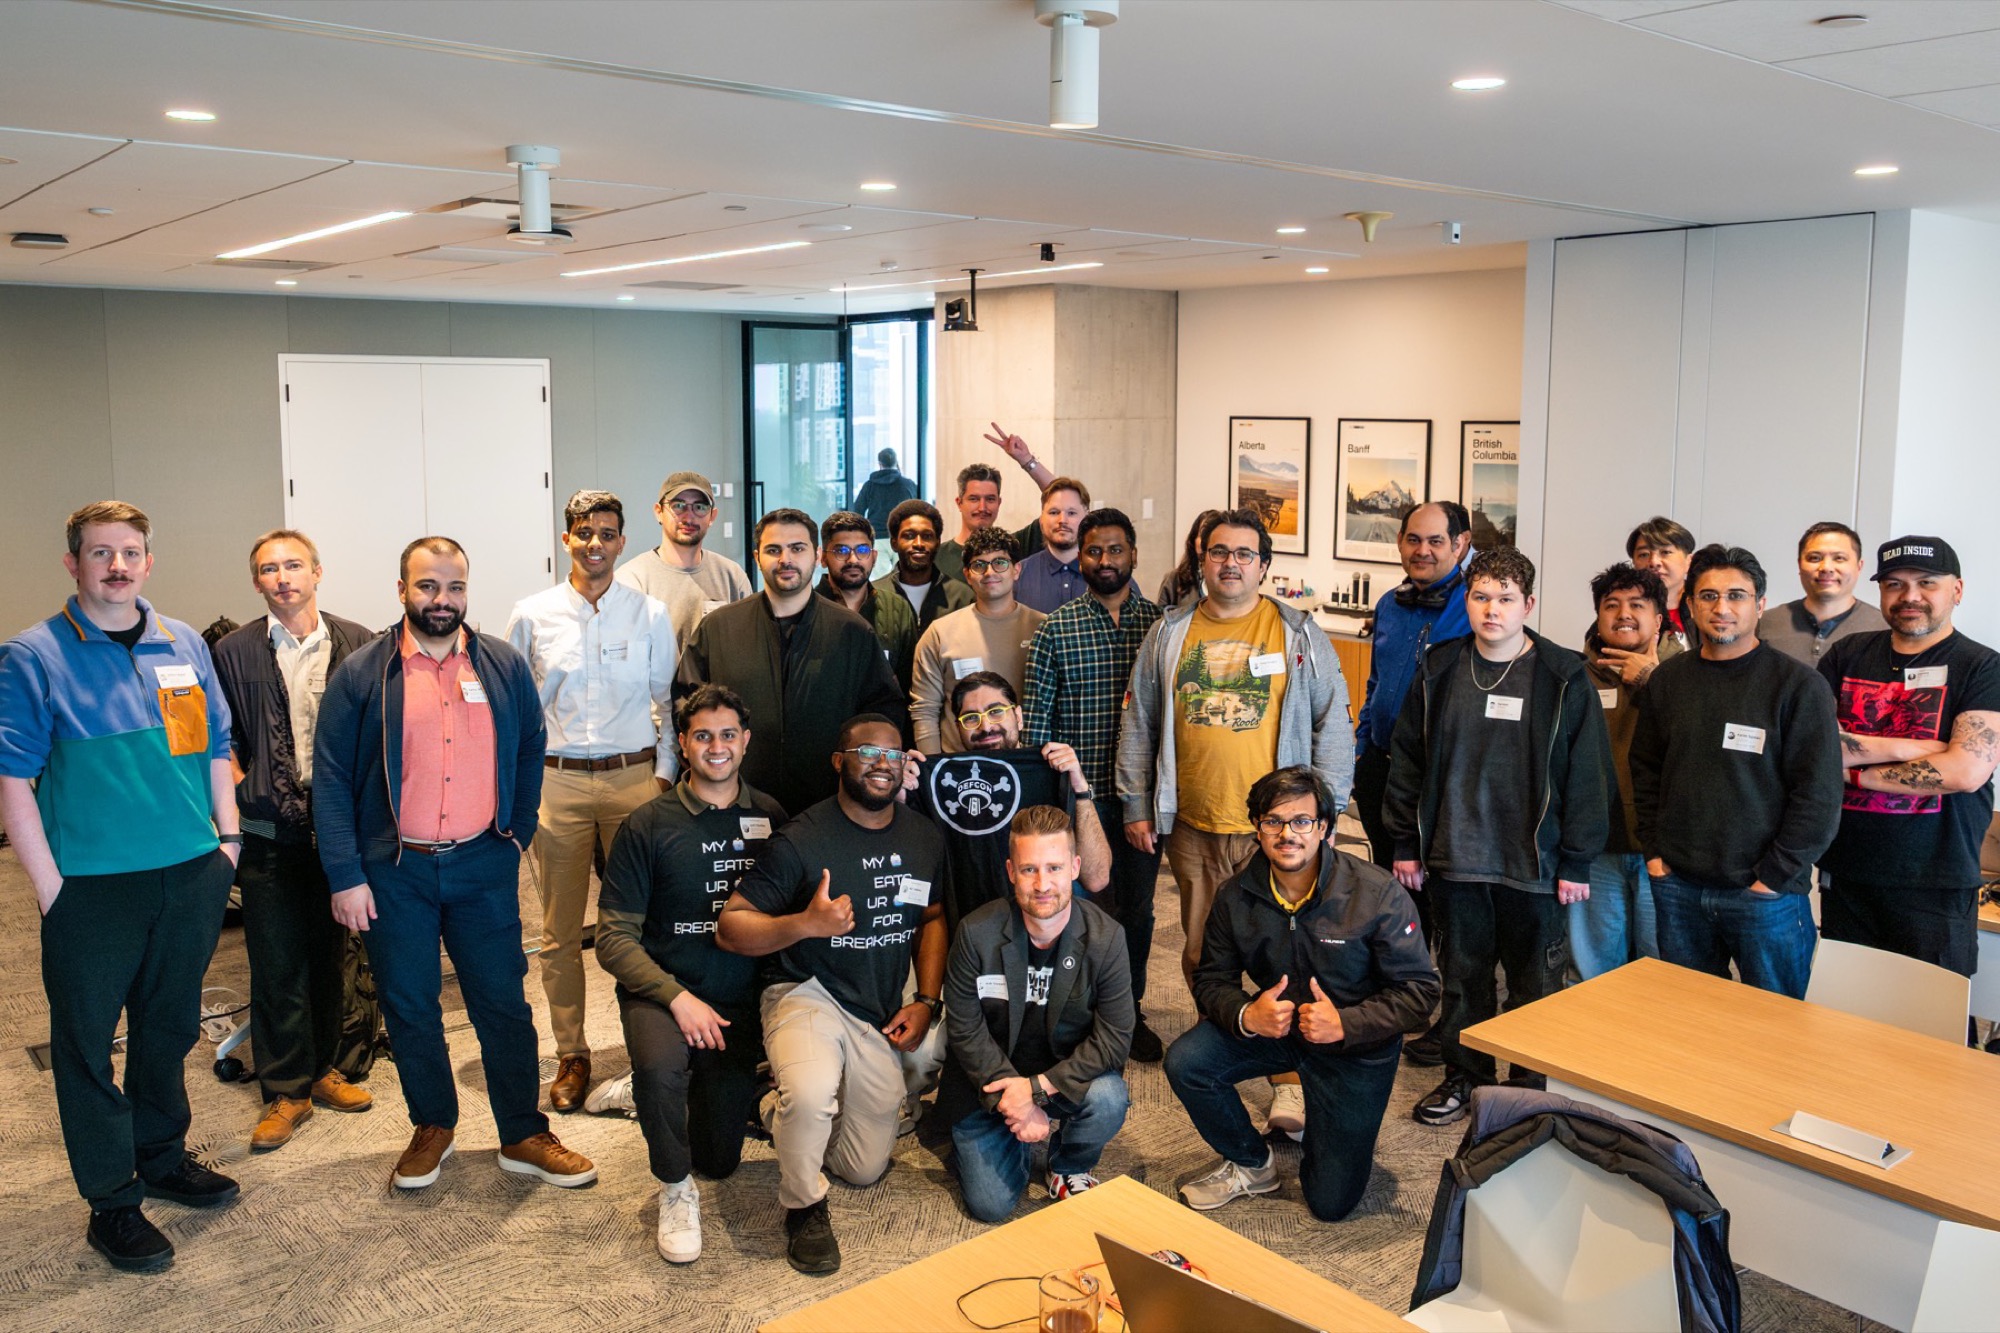
DEFCON Toronto (DC416), Co-organizer
Toronto · 2025 to Present
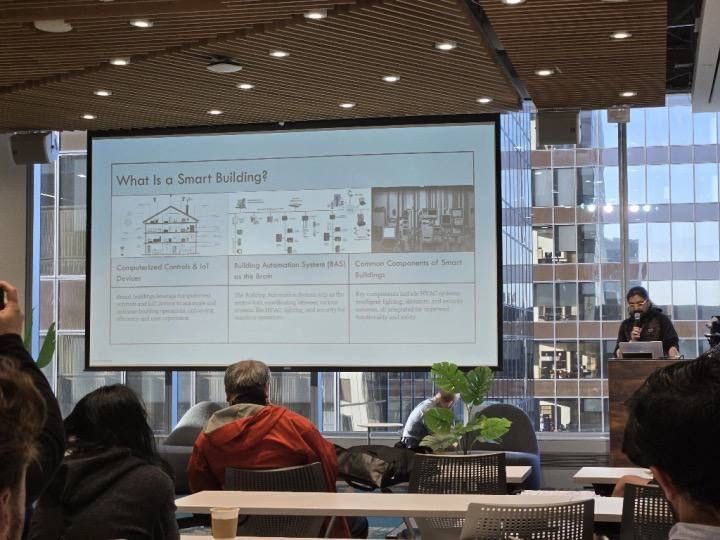
I find researchers and presenters, help them shape their talks and workshops, and program the monthly meetups for Toronto's security community, including the AI Fight Club workshop at Palo Alto Networks for 200+ practitioners. Also on the organizing committee for TASK, where I spoke in 2025 and 2026.
HackerOne, Security Researcher
Remote · Feb 2022 to Present
120+ validated vulnerabilities across Fortune 500 programs, including severe findings on PayPal, Airbnb, Sony, Booking.com and AT&T. Focus on authorization bypass, privilege escalation, race conditions and multi-step business-logic chains.